
ISО/IЕC 27001:2022 has been published
What has changed?
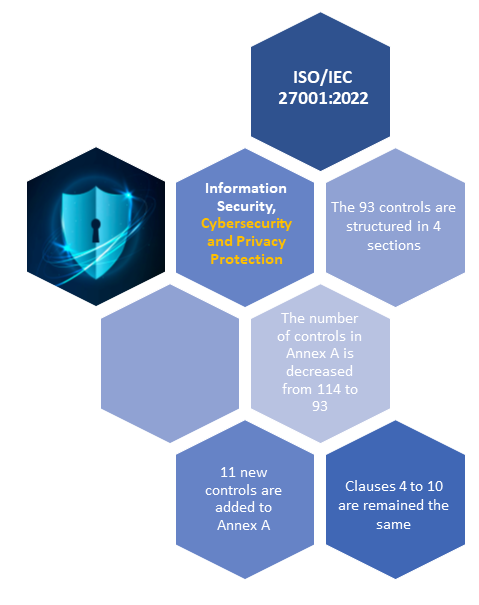
The title, of course. The main part of ISO/IEC 27001, namely clauses 4 to 10 remain unchanged. These clauses include the scope, normative references, the context of the organization, leadership, planning, support, operation, performance evaluation and improvement.
Certain editorial corrections and changes have been made to harmonize performance in accordance with the ISO approach, namely:
- Numbering has been restructured;
- Requirements have been introduced to define the processes necessary to implement an ISMS and their interactions;
- A specific requirement has been stated to name organizational roles, connected to information security in the structure of the organization;
- A new clause 6.3 – Planning of changes has been added;
- There is a new requirement for communication, as part of clause 7.4;
- New requirements to establish criteria for operational processes and the implementation of process control have been added.
- Organizational controls;
- Controls for human resources management;
- Controls connected to physical security;
- Technological controls.
- Threat intelligence
- Monitoring of physical security
- Data masking
- Information security for use of cloud services
- Monitoring activities
- ICT readiness for business continuity
- Data leakage prevention
- Configuration management
- Web filtering
- Information deletion
- Secure coding.
- Control type (preventive, detective, corrective)
- Information security properties (confidentiality, integrity, availability)
- Cybersecurity concepts (identify, protect, detect, respond, recover)
- Operational capabilities (governance, asset management, etc.)
- Security domains (governance and ecosystem, protection, defense, resilience)
What comes next?
Organizations planning initial certification should develop an Information security management system, taking into account the requirements of ISO/IEC 27001:2022. Organizations continuing their certification should plan a transition to the new version within 3 years. After October, 2025 audits for initial certification and recertification in accordance to ISO/IEC 27001:2013 are not going to be conducted.
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


