
Transition to the Requirements of ISO/IEC 27001:2022
CHANGES IN MANAGEMENT SYSTEMS
In connection with the latest version of ISO/IEC 27001:2022, CONSEJO Ltd. offers consulting services for updating existing Information Security Management Systems (ISMS) as well as improving the overall management of business processes.
All organizations wishing to remain ISO/IEC 27001 certified will be required to update their Management Systems. A transition audit must be performed either in conjunction with an already scheduled surveillance/recertification review or in a separate audit within the transition period.
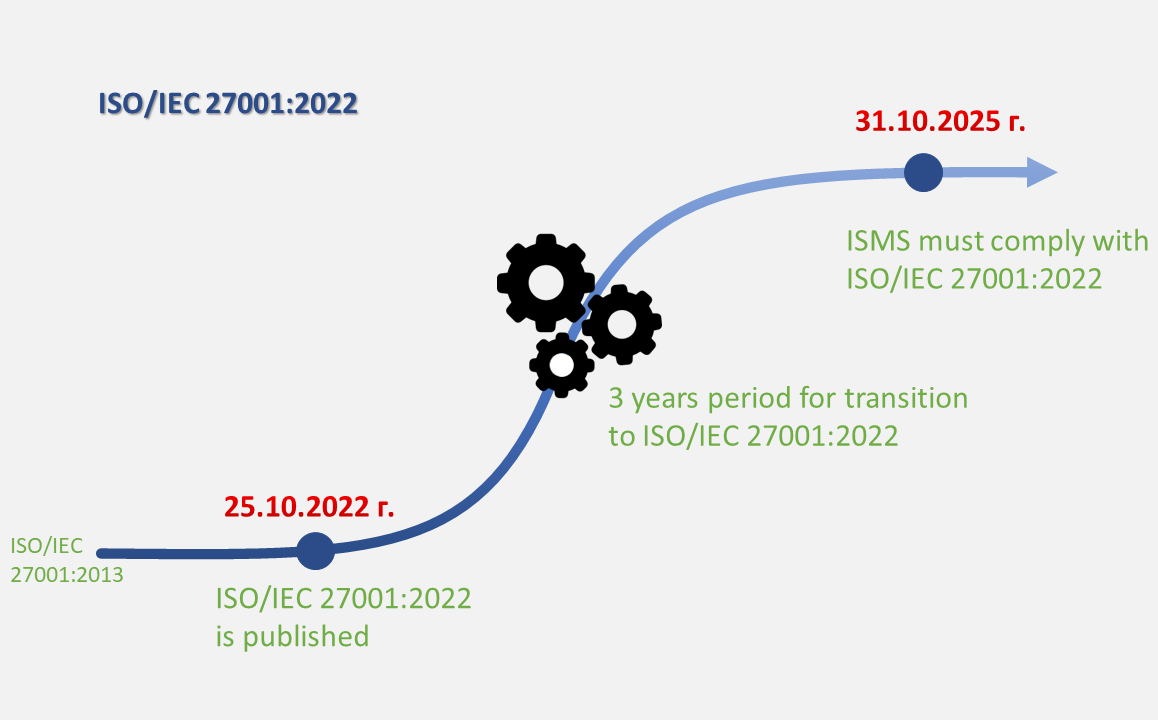
Timelines to Transition:
• October 31, 2022 – beginning of the transition period;
• April 30, 2023 – after this date all initial (new) certifications must be conducted against ISO/IEC 27001:2022. It is also recommended that management systems subject to recertification audits comply with the new version;
• October 31, 2025 – Transition period ends. After this date, ISO/IEC 27001:2013 Certificates will no longer be valid.
During the 3-year transition period, both versions of the ISO/IEC 27001 standard are valid. Certified organizations must plan and take the necessary actions for the transition and audit to take place within the transition period.
What should you do next?
Certified organizations must bring their information security management system into compliance with the requirements of ISO/IEC 27001:2022 and a transition audit must be conducted.
For this purpose, organizations need to:
• Analyse the changes and prepare a transition plan to the new version of ISO/IEC 27001:2022;
• Update the ISMS documentation, the Declaration of applicability, etc. related documents;
• Review and update the risk assessment and risk impact plan.
• Implement the new and changed controls in accordance with Appendix A and the Declaration of Applicability;
• Perform an internal audit of ISMS;
• Conduct a management review to assess the effectiveness of the changes made to the ISMS;
• Contact the certification body to schedule the transition audit.
According to the needs of your company, CONSEJO offers to:
2. Prepare a plan for transition to the new version of ISO/IEC 27001:2022;
3. Update of the available documentation from ISMS according to ISO/IEC 27001:2022;
4. Train the staff in order to apply the requirements of ISO/IEC 27001:2022;
5. Conduct internal audits according to ISO/IEC 27001:2022;
6. Consult and assist you during a supervisory, recertification or unscheduled audit for certification according to the new version of ISO/IEC 27001:2022.
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


