
Service Organization Control Type 2
Companies are facing a growing threat environment, making information and data security a top priority. A data breach can cost millions, not to mention the reputational damage and loss of customer trust. Cybersecurity requires defining frameworks – guiding principles and best practices that companies must follow to ensure information security. SOC 2, or Service Organization Control Type 2, is an auditing and attestation framework developed by the American Institute of Certified Public Accountants (AICPA). Its main purpose is to ensure that service providers store and process customer data in a secure manner.
While standards such as ISO/IEC 27001 and PCI DSS have strict requirements regarding cybersecurity controls, SOC 2 does not prescribe a fixed set of controls; insteat, each organization designs and implements controls appropriate to its services, operating model, and risk profile. An independent auditor is then appointed to assess whether these controls are suitably designed and operating effectively in accordance with SOC 2 requirements. Following the audit, the auditor issues a report describing how well the organization’s systems and processes meet the applicable Trust Service Criteria.
SOC 2 defines the requirements for the management and storage of customer data based on five criteria for trustworthiness of services (Trust Service Criteria, TSC):
Security. Generally speaking, the principle of security requires the protection of data and systems against unauthorized access. This may require implementing some form of access control, implementing firewalls with strict rules for inbound and outbound traffic, implementing intrusion detection and recovery systems, and using multi-factor authentication.
Confidentiality. Data is considered confidential if only a certain group of people have access to it. This may include application code, usernames and passwords, payment card data, or business plans, etc. To comply with this principle, confidential data must be encrypted, both at rest and in transit, following the principle of least privilege, i.e. providing the minimum rights people need to do their jobs.
Availability. This requires building systems that ensure the availability of services in line with business requirements and agreed service levels (SLAs), resistant to errors and high traffic. This principle requires organizations to use network monitoring systems and create and use disaster recovery plans.
Privacy. The collection, storage, processing and disclosure of any personally identifiable information (PII) must adhere to the organization's data use and privacy policy, along with the terms set forth by the AICPA in the Generally Accepted Privacy Principles (GAPP). The organization must enforce strict controls to protect PII from unauthorized access.
Processing integrity. Systems processing must be complete, valid, accurate, timely, and authorized. Controls typically include input validation, job processing controls, reconciliations, monitoring, and quality assurance procedures.
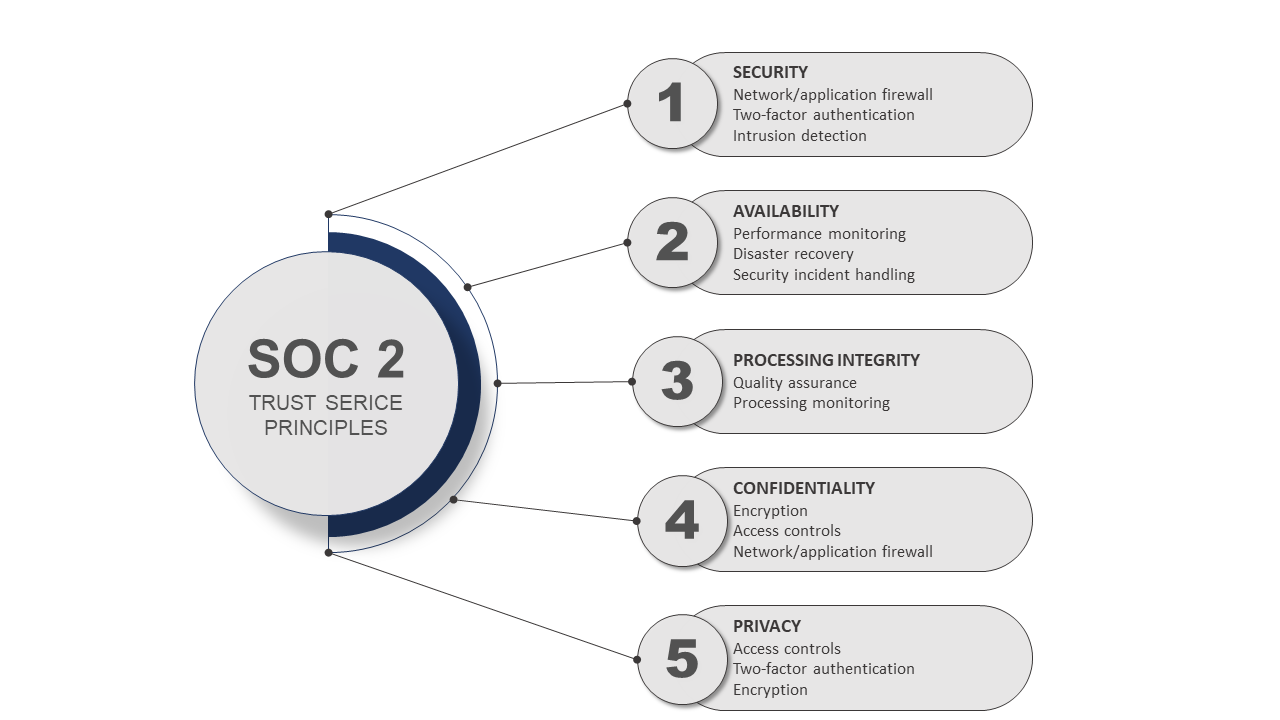
To satisfy the five principles of TSC, you must answer the following questions regarding:
- Information security: how is data protected from unauthorized access and use?
- Logical and physical access control: how is logical and physical access managed and restricted to prevent unauthorized use?
- System operations: what are and how are the systems for detecting and mitigating process deviations managed?
- Change Management: How do you implement a controlled change management process and prevent unauthorized changes?
- Risk Mitigation: How is the risk of business and service disruption identified and mitigated?
Types of SOC 2 reports
SOC 2 reports are of two types:
- SOC 2 Type I assesses the company's controls at a specific point in time. They answer the question: Are the security controls properly designed?
- SOC 2 Type II evaluates how these controls function over a period of time, typically 3 to 12 months. They answer the question: Are the security controls a company has in place functioning as intended?
To choose between the two, consider your goals, costs, and any constraints, such as time.
SOC 2 Audit Results
Every organization that has passed a SOC 2 audit receives a report, regardless of the conclusions of the audit. Here are the terms auditors use to describe audit results:
- Unqualified Opinion: the organisation has passed the audit without reservations and restrictions. It means the controls the auditor tested were designed and operating exactly as they should be
- Qualified Opinion: the organisation passes the audit, but some areas require attention. During the audit period, either one or more controls included in the assessment were not adequately designed or implemented.
- Disclaimer Opinion: the organisation didn’t provide the auditor with enough information, and they were unable to form an opinion on whether you were SOC 2 compliant.
- Adverse Opinion: the organisation failed one or more of the compliance standards. Considered the lowest opinion in a SOC 2 report, adverse opinions tell customers they shouldn’t place trust in an organization’s systems
Who needs a SOC 2 report?
If you are a service organization that stores, processes or transmits any kind of customer data, you will likely need to be SOC 2 compliant because:
- SOC 2 requirements help your company establish internal security controls – a foundation of security policies and processes that can help your business expand securely.
- you build trust with your customers.
Often service organizations need a SOC 2 report because their customers require it. Customers need to know that their sensitive data is safe. The SOC 2 report can also be key to expanding sales and entering a larger market because it:
- signals to customers the level of maturity of your organization;
- demonstrates your commitment to security;
- provides a strong competitive advantage.
Simply put, a SOC 2 audit is important for two reasons. First, obtaining a SOC 2 report helps your business maintain best-in-class security standards. And second, it can unlock significant growth opportunities.
Service Organization Control Type 2
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


