
Phishing Simulations for Employees
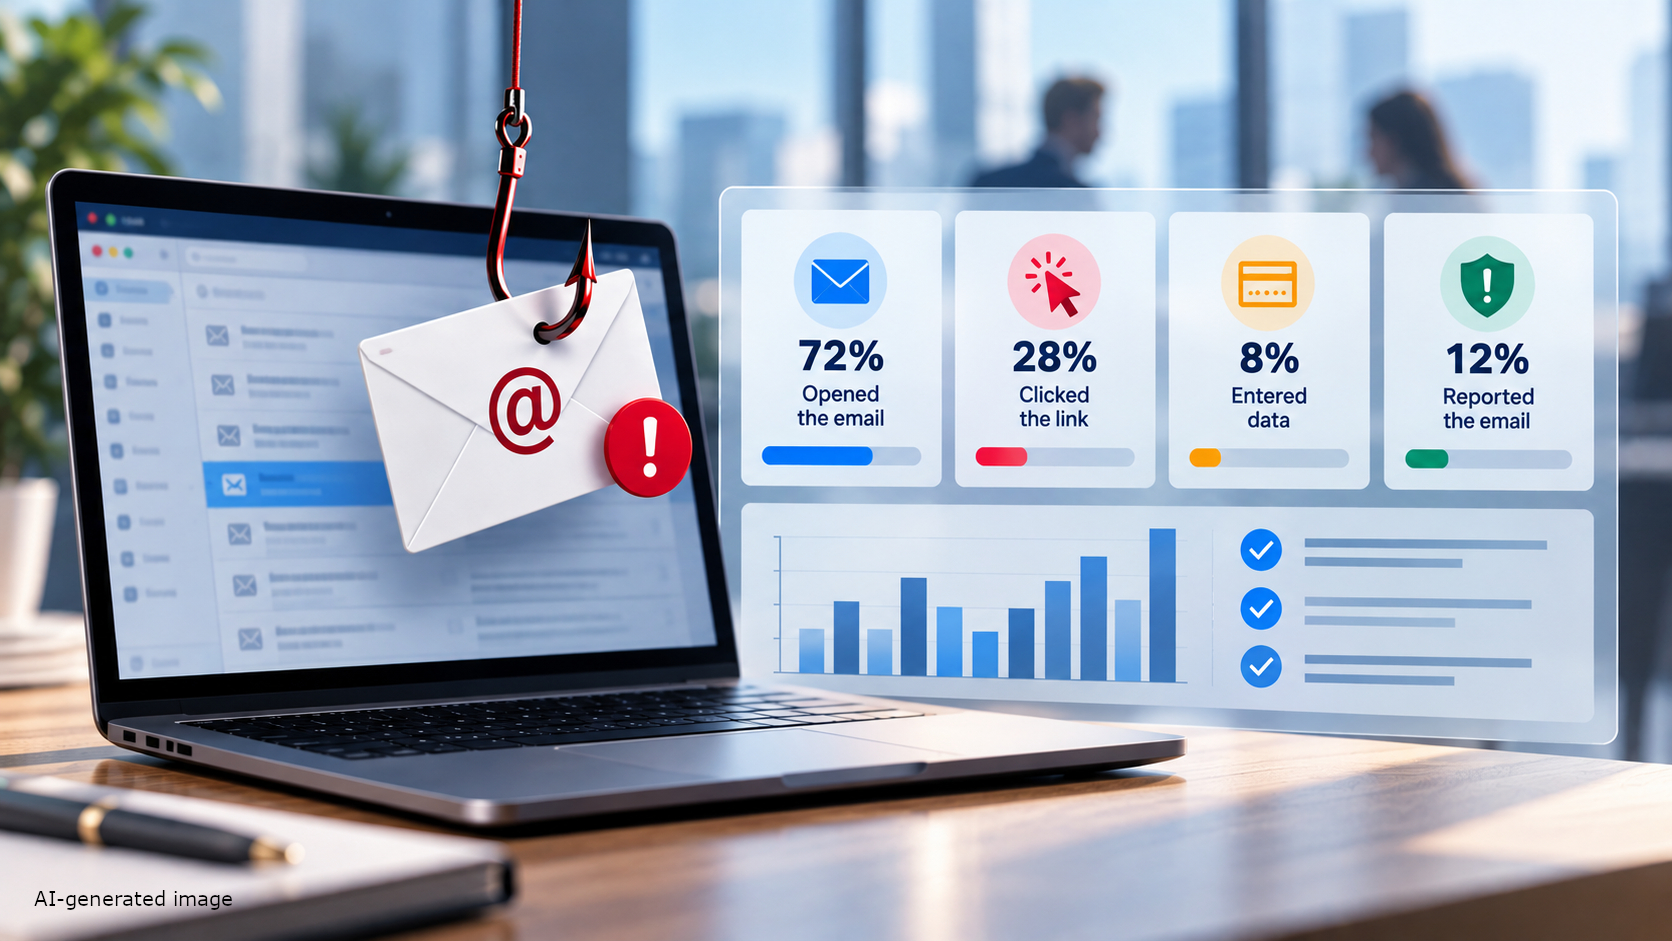 CONSEJO conducts controlled phishing campaigns that resemble real attacks but do not cause harm. After the campaign, you receive a clear report showing how many employees opened the message, how many clicked, how many entered data and how many reported the message. The report also indicates what needs to be done to reduce the risk.
Why Conduct a Phishing Simulation?
- Measurable risk instead of assumptions. You see how employees actually behave, rather than simply whether they have attended training.
- Targeted training. You focus your efforts on the departments and individuals who need it.
- Evidence of compliance. The report serves as evidence of awareness measures during an inspection or audit.
- A culture of reporting. Employees learn not only to avoid clicking but also to report suspicious messages promptly.
Compliance with Requirements
- Bulgarian Cybersecurity Act and NIS2: The Directive requires basic cyber hygiene practices and cybersecurity training (Article 21), as well as training for management (Article 20).
- ISO/IEC 27001: Control A.6.3 requires information security awareness, education and training.
- DORA: Financial organisations must conduct digital operational resilience awareness and training programmes for their employees.
How It Works
- Scope and rules. We agree on which employees will participate, which scenarios are permitted and who within the organisation will be informed.
- Scenarios. We prepare realistic messages tailored to your industry and the attacks currently occurring in Bulgaria: fake courier notifications, invoices, banks, Microsoft 365 password requests and others.
- Campaign. We send the messages in stages to prevent employees from warning one another.
- Report and recommendations. You receive results by department and specific measures to be implemented over the following months.
- Training. Practical training on recognising phishing emails.
- Repetition. We recommend conducting campaigns every 3 to 6 months to monitor progress.
What You Receive
- A report with the results: opened messages, clicks, entered data and reported messages
- Comparisons between departments and, for repeated campaigns, over time
- Recommendations for technical and organisational measures
- Brief training materials for employees
- A management summary suitable for reporting under the Bulgarian Cybersecurity Act or for a management review under ISO/IEC 27001.
Personal Data and Ethics
The simulation is conducted according to previously agreed rules and with the involvement of management. The results can be presented in an aggregated form without identifying individual employees. The aim is not to find someone to blame, but to reduce the risk to the organisation.
Frequently Asked Questions
Do employees need to know in advance?
Not about the specific campaign, as this would make the results unrealistic. However, we recommend that employees be informed that the organisation conducts periodic awareness assessments.
How long does it take?
Preparation takes approximately 1 to 2 weeks, while the campaign itself usually lasts 1 to 2 weeks.
Is it suitable for small organisations?
Yes. The smaller the organisation, the greater the impact of a single successful phishing email.
Can it be combined with other services?
Yes. Phishing simulations are often conducted together with penetration testing or as part of preparations for compliance with NIS2 and the Bulgarian Cybersecurity Act.
Phishing Simulations for Employees
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


