
NIST SP 800-53 Security and Privacy Controls for Information Systems and Organizations
NIST SP 800-53 is designed to provide a framework of elements, strategies, systems, and controls for each organization's cybersecurity needs and priorities. Because it does not cite or require the use of specific tools, mechanisms, or manufacturing brands, it is flexible and up-to-date regardless of emerging new technologies, systems, or cloud resources.
Who is NIST 800-53 intended for?
Compliance with this standard is required for any organization that works with federal information systems, in conjunction with US agencies, or with the US government.
NIST SP 800-53 Controls
According to NIST SP 800-53 Rev. 5 controls are "descriptions of protective mechanisms appropriate to achieve the organization's specific security and privacy objectives. Controls are selected and implemented by the organization to satisfy system requirements."
Control groups contain basic controls and directly related additional controls ("control enhancements"). Additional controls contain more detail and specificity with respect to the base control. They should be applied in systems and work environments that require more reliable protection.
The controls are systematized in 20 groups that provide operational, technical and management measures to ensure the confidentiality, integrity and security of information systems.
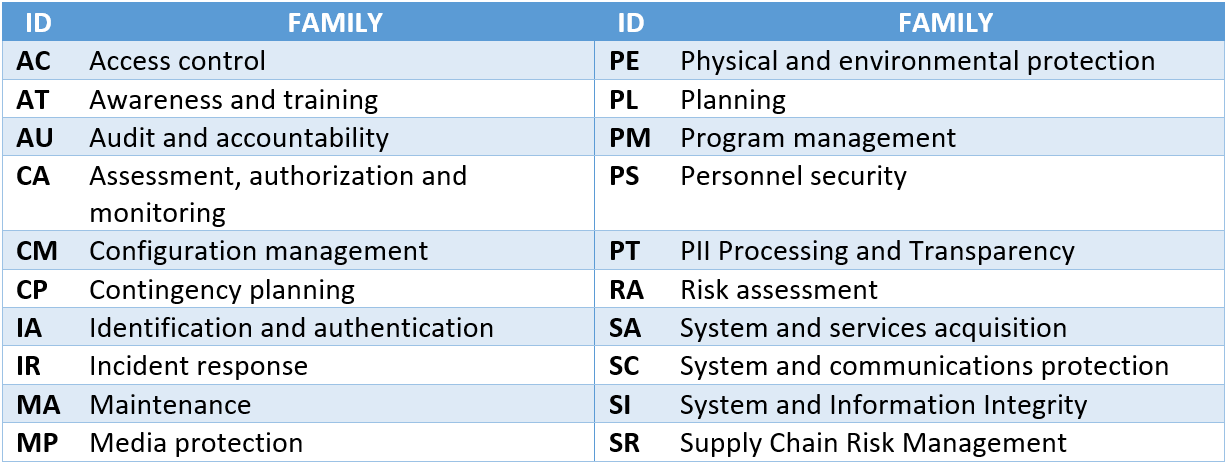
Since NIST SP 800-53 Rev. 5 has 20 control families, it is important to prioritize an organization's efforts based on the areas of greatest impact on its security and the security of its stakeholders. In an environment where many employees are working on potentially unauthorized networks and applications, including from their personal devices, five groups of controls are of particular importance to ensure adequate protection: access control, employee awareness and training, configuration management , audits and monitoring.
Can NIST SP 800-53 Improve Your Organization's Security System?
Yes. Although it was originally intended for use by US federal government agencies, it can help organizations in all industries improve the security of their information systems. NIST SP 800-53 contains a set of security and privacy safeguards for all types of computing platforms, cloud systems, mobile systems, industrial systems, and Internet of Things (IoT) devices. In many cases, implementing NIST SP 800-53 will help organizations ensure compliance with other cyber risk and information security regulations that use NIST as a reference framework.
NIST SP 800-53 Security and Privacy Controls for Information Systems and Organizations
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


