
New version of ISO/IEC 27002
 On 15 February 2022 the international organization ISO published the new version of ISO/IEC 27002 "Information security, cybersecurity and privacy protection - Information security controls".
The information security management standard ISO/IEC 27001 "Information technology. Security methods. Information security management systems. Requirements' and its Code of Good Practice (ISO/IEC 27002) were last updated almost 10 years ago. A revised version of ISO/IEC 27001 is expected in 2022.
What is changing in ISO/IEC 27002?
The first thing that is immediately noticeable is the change in title - "Code of Good Practice" has been replaced with "Information Security Controls", which better reflects the purpose of the standard - to provide guidance on implementing a reference set of information security controls. The standard is considerably longer than the previous version and the controls themselves have been regrouped and updated. The changes are aimed at simplifying implementation: the number of controls has been reduced from 114 to 93 (by merging), they are divided into 4 groups instead of the previous 14. There are 11 new controls and none of the previous controls have been removed.
The new ISO/IEC 27002:2022 has 93 controls distributed in 4 groups, and two annexes:
- Organizational (clause 5);
- Human Resources related (clause 6);
- Physical security related (clause 7);
- Technological controls (clause 8);
- Annex A - Use of Attributes;
- Annex B - Compliance with ISO/IEC 27002:2013.
The new controls are:
- Threat Intelligence;
- Information security when using cloud services;
- ICT readiness for business continuity;
- Physical Security Monitoring;
- Configuration Management;
- Information Erasure;
- Data Masking;
- Data Leakage Prevention;
- Monitoring Activities;
- Web filtering;
- Secure Code Writing.
Controls now have five "attribute" to make them easier to categorize:
- Control type (preventive, detecting, correcting);
- Information security properties (confidentiality, integrity, availability);
- Cybersecurity concepts (identify, protect, detect, respond, recover);
- Operational capabilities (governance, asset management, etc.);
- Security domains (governance and ecosystem, protection, defense, resilience).
How will this affect organizations implementing ISO/IEC 27001?
As part of the risk management process, ISO/IEC 27001:2013 allows you to select controls as long as you compare them to Annex A and document the reasons for your selection. The 2022 version of ISO/IEC 27001 is expected to be broadly similar to the 2013 version, with a new version of Annex A that will mirror the controls in the new ISO/IEC 27002.
Until the new version of ISO/IEC 27001 is published, the Statement of Applicability should still refer to Annex A of ISO/IEC 27001:2013, and the controls in ISO/IEC 27002:2022 will be an alternative set that you will need to compare to the existing Annex A.
What does this mean for organisations already certified to ISO/IEC 27001:2013?
Contrary to most expectations, ISO will not release an entirely new ISO/IEC 27001:2022. Instead, there will be an amendment to ISO/IEC 27001:2013 (called ISO/IEC 27001:2013/DAMD 1) in which Annex A will be replaced with a normative version of the 93 new controls from ISO/IEC 27002:2022.
There is usually a two-year transition period for certified organisations to revise their management system to comply with the new version of the standard. In this case, however, there is no need to wait for the release of the updated ISO/IEC 27001:2013/DAMD 1 as it will be fully compliant with the controls described and grouped in the already published ISO/IEC 27002:2022.
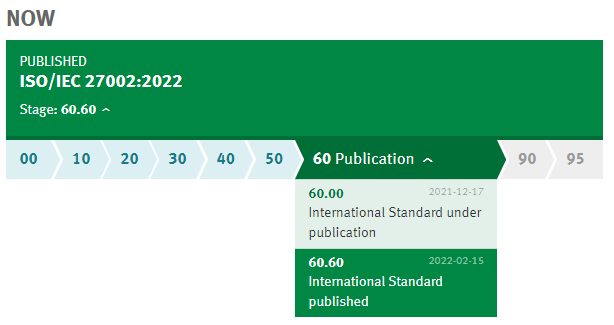
Source: iso.org
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


