
How NIS 2 relates to ISO/IEC 27001
 Directive (EU) 2022/2555 aims to strengthen cybersecurity in the member states of the European Union and will come into force on 17 October 2024. As the deadline for implementing the directive approaches, organisations that fall within its extended scope are preparing to comply with the new regulatory requirements. The Directive, known as NIS 2, aims to achieve a high common level of cyber security across Member States. But it also applies to entities outside the Community - organisations operating in the EU. By understanding the relationship between NIS 2 and ISO/IEC 27001, organizations can optimize their compliance efforts and increase their protection against cyber threats.
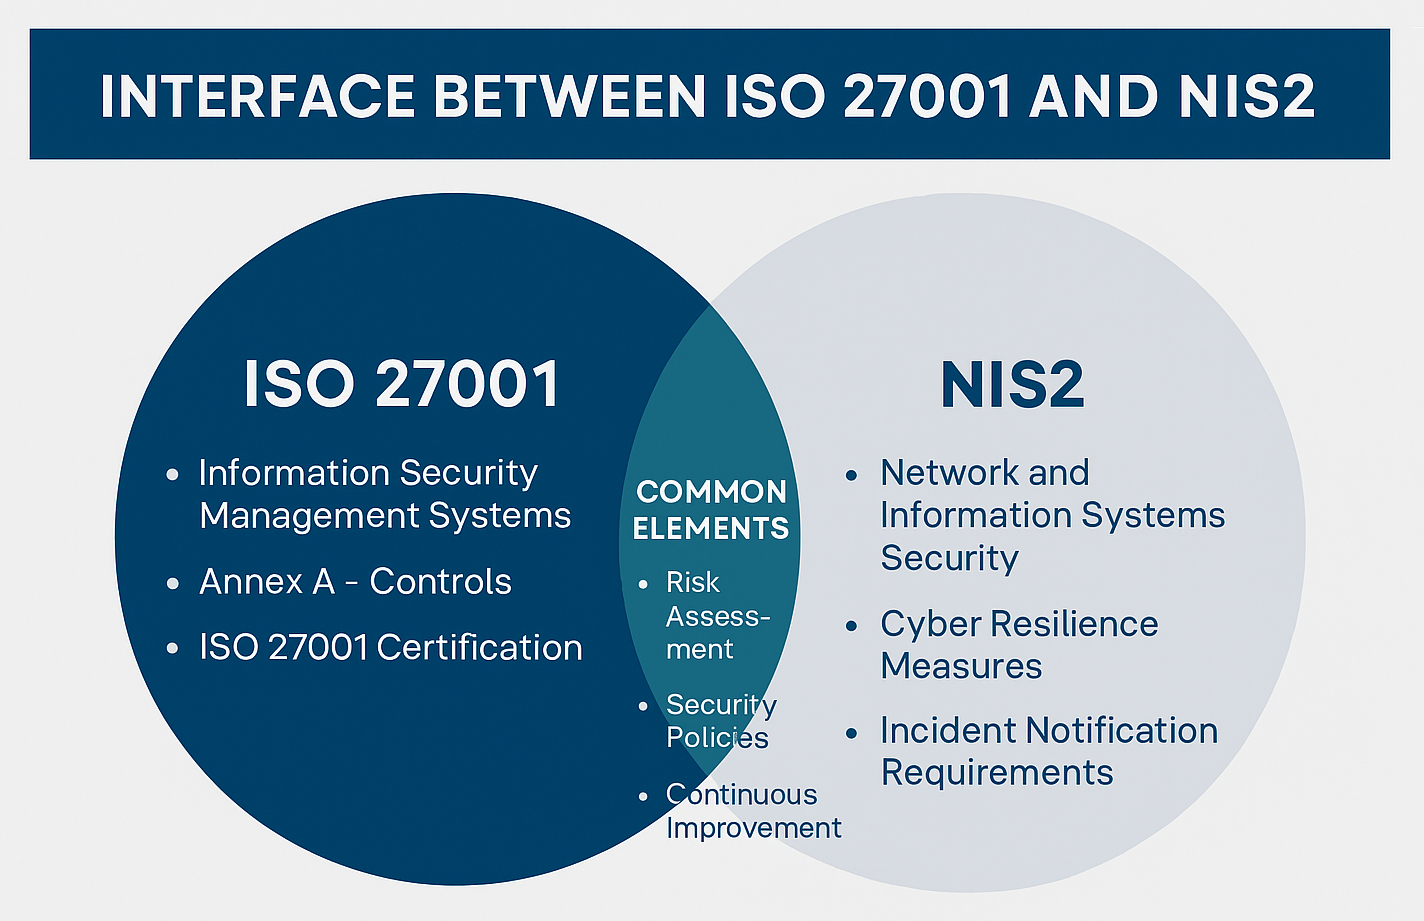
On the other hand, ISO/IEC 27001 is an established international standard that provides a voluntary framework for organisations to establish, implement, maintain and continually improve an Information Security Management System (ISMS). Complying with ISO/IEC 27001 means implementing a robust information security management system that protects the confidentiality, integrity and availability of information assets.
Bringing cyber security into compliance with NIS 2 can require significant effort, but ISO/IEC 27001 eases the transition process. Implementing a cyber security and information security management system to ISO/IEC 27001 provides an effective management framework that can serve as a foundation for NIS 2 compliance.
The stages of implementation of requirements may include
1. Status assessment: an evaluation of the organisation's existing policies, procedures, technologies and practices. Identify areas of risk, areas for improvement and changes required to achieve compliance.
2. Establishing policies and procedures: ISO/IEC 27001 provides a structured approach to managing information security risks, covering policies, procedures, technical measures and employee awareness programmes. Thе standard is an essential tool to prepare an organisation for NIS 2 compliance.
3. Compliance monitoring: Successful implementation of policies and procedures can be ascertained by conducting an internal audit of business processes. The audit is carried out by monitoring all processes related to the implementation of the requirements. Its main goals relate to reviewing and analyzing the compliance of the processes, mechanisms and controls implemented by the organization to protect information assets with regulatory requirements and helping the organization make necessary adjustments to policies and procedures to ensure that the ISMS is effective and up-to-date in the context of emerging threats and changes in the environment.
Using ISO/IEC 27001 to meet NIS 2 requirements increases the level of cybersecurity organizations need to meet new regulatory requirements. This approach not only facilitates the compliance process, but also strengthens the overall security of the organization's information assets.
CONSEJO offers a variety of services to help you achieve compliance with the NIS 2 directive and the ISO/IEC 27001 international standard. Our experience and expertise in cybersecurity and information security management will help you improve your cybersecurity posture and achieve sustainable regulatory compliance. With our support, you can protect your information assets, minimize risks and meet regulatory requirements in an effective and efficient manner. Contact us to discuss your questions and offer a customized solution for your organization.
Directive (EU) 2022/2555 - EUR-Lex (europa.eu)
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


