
ISO/IEC 27017 – Information Security Standard for Cloud Services
In the era of digital transformation, an increasing number of organizations are shifting their operations, data, and infrastructure to the cloud. While this shift brings many advantages—flexibility, scalability, and cost savings—it also introduces new risks, particularly related to information security. That’s where the international standard ISO/IEC 27017:2015 comes in: a Code of practice for information security controls based on ISO/IEC 27002 for cloud services.
What Is ISO/IEC 27017?
ISO/IEC 27017 is an international standard jointly developed by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC). It provides guidelines and best practices for managing information security in cloud environments—for both service providers and customers.
Designed as an extension of ISO/IEC 27002, the standard tailors and expands security controls to address the unique characteristics of cloud technologies. It is particularly valuable for organizations that currently use or plan to use cloud infrastructure (IaaS), platforms (PaaS), or software services (SaaS).
Main Objectives of ISO/IEC 27017
- Build trust between cloud providers and customers
- Define and assign clear responsibilities between involved parties
- Support compliance with legal and regulatory requirements
- Strengthen security for virtual machines, network resources, and data within cloud environments
Structure and Content
The standard consists of two primary components:
- Extended guidance on existing controls from ISO/IEC 27002
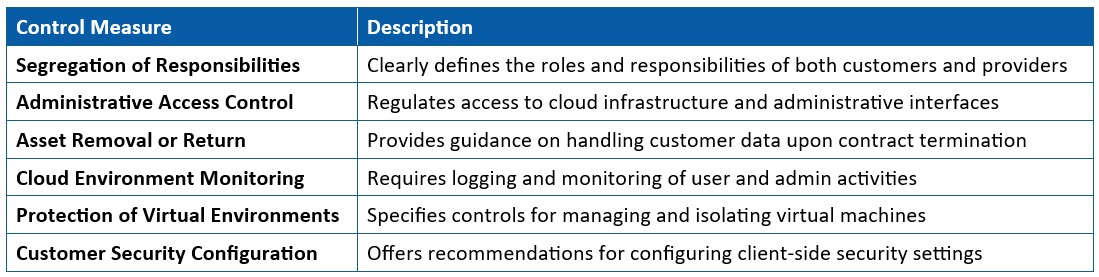
- Seven additional cloud-specific control measures
Key cloud control measures
Who Is It For?
- Cloud service providers – to demonstrate the delivery of secure and reliable services
- Cloud service customers – to better manage security risks and supplier expectations
- IT companies and financial institutions – especially those handling sensitive or regulated data
- Organizations certified under ISO/IEC 27001 – as a cloud-specific extension of their security framework
Benefits of Implementing ISO/IEC 27017
- Strengthened protection of cloud-based data and systems
- Clearer understanding and agreement between service providers and customers
- Reduced risk of data breaches and unauthorized access
- Better documentation and traceability of security-related actions
- Increased competitive advantage and customer trust on the global market
Part of the ISO/IEC 27000 Family
ISO/IEC 27017 complements and extends the widely adopted ISO/IEC 27000 series of information security standards:
- ISO/IEC 27001 defines the core framework for building and maintaining an Information Security Management System (ISMS)
- ISO/IEC 27002 provides detailed implementation guidance for security controls
- ISO/IEC 27017 adds specialized cloud security recommendations, clarifying responsibilities for both cloud providers and customers
- ISO/IEC 27018 focuses on the protection of personally identifiable information (PII) in cloud environments and privacy compliance
ISO/IEC 27017 is a vital resource for any organization using or offering cloud services. By aligning with this international standard, businesses not only enhance their cybersecurity posture but also build stronger trust with partners, clients, and regulators. In today’s digital world—where data is among the most valuable assets—adopting proven security practices like ISO 27017 is no longer optional; it’s a critical requirement for long-term resilience and success.
Implementation of management standards
CONSEJO Ltd. is a consulting company with over 20 years of practical experience in the development, implementation and maintenance of management systems in accordance with international standards and regulatory requirements. The company provides consulting services in the areas of quality management, environmental management, occupational health and safety, food safety, information security, cybersecurity, risk management and sustainable development. Our expertise covers standards and schemes such as ISO 9001, ISO 14001, ISO 45001, ISO 22000, ISO/IEC 27001, IFS Food, BRCGS and HACCP, as well as consulting services related to NIS2, DORA, GDPR and EcoVadis.
The CONSEJO team has been involved in over 1,500 projects for organizations across various sectors of the economy, including manufacturing, construction, energy, information technology, transport, trade, the food industry and services. Our approach focuses on developing management systems that work effectively in practice, tailored to the specific characteristics and needs of each organization. We work closely with our clients, providing consulting support, staff training and assistance during implementation. We strive to deliver high-quality services within the agreed deadlines and solutions that support successful certification and create long-term value for businesses.


